PCI Compliance for Gyms: What Owners Need to Do

If your gym takes credit or debit cards in any form, you must comply with PCI DSS, the Payment Card Industry Data Security Standard. It makes no difference whether that is a front-desk terminal, an online signup form, or monthly dues billed automatically. Size doesn’t matter either. Using a payment processor shrinks the work, but it doesn’t remove your responsibility. This guide shows which gyms are covered, which self-assessment questionnaire (SAQ) fits your setup, and how to stay compliant year after year.
Getfitnessflow
Simplify gym payment management
Fitness Flow brings gym billing and management tools together, helping owners reduce the number of software subscriptions they need to manage.
TL;DR
- Every gym that accepts cards must comply with PCI DSS, whether it handles five card payments or five million.
- Outsourcing payments to a compliant processor reduces your scope, but you still validate compliance every year, usually with an SAQ.
- Your SAQ depends on how you take payments: outsourced online checkout, standalone terminals, or a web-based virtual terminal each point to a different form.
- You must confirm that every provider touching card data is compliant, and recheck it at least annually.
- Fewer payment tools means fewer vendors to track and a smaller area to protect.
Table of Contents
- Does PCI compliance apply to your gym?
- What PCI DSS actually requires
- Which SAQ does your gym fill out?
- If a processor handles your payments, are you off the hook?
- A realistic path to compliance
- Common gym mistakes that expand your PCI scope
- What does PCI compliance cost a gym?
- Our perspective
- Simplify the tools behind your payments
- FAQ
- Sources
Does PCI compliance apply to your gym?
Yes. All businesses that store, process or transmit cardholder data must be PCI compliant, including those that only take card numbers over the phone. The in-scope cards are debit, credit and prepaid cards branded American Express, Discover, JCB, Mastercard or Visa. That covers essentially every membership business.
The rule comes from the card brands, not from a law. Visa requires every organization that stores, transmits or processes its account data to comply. The standard covers all payment channels: card present, mail and telephone orders, eCommerce and in-app. In practice your merchant agreement with your acquirer (the bank behind your processing account) is where the obligation lives, and the acquirer is who asks you for proof.
For a gym, that means every one of these touches PCI:
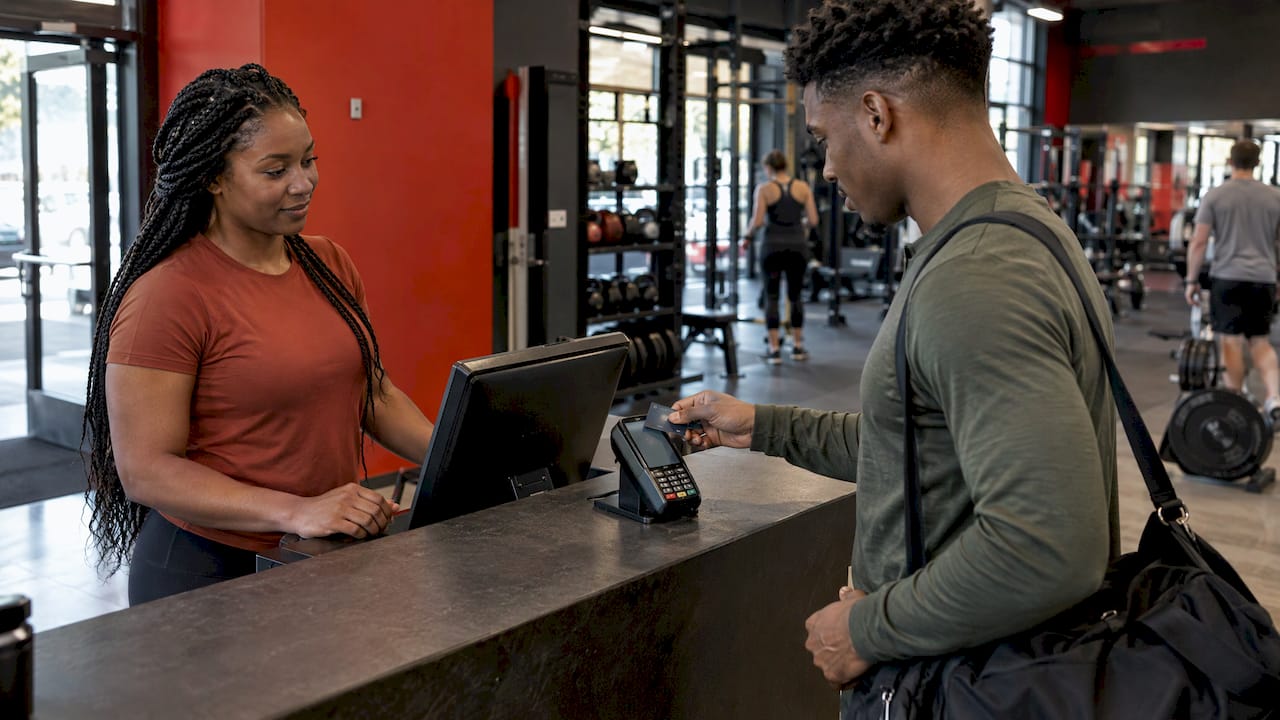
- The card reader or terminal at the front desk
- Online membership signup and class or session purchases
- Recurring dues billed to a card on file
- Retail sales of drinks, apparel and day passes
- Phone payments taken by staff, and paper forms with card numbers written on them
That last pair is where gyms most often get into trouble. A card number scribbled on a paper billing form or typed into a spreadsheet puts that sheet, the computer and anyone with access into your compliance picture.
What PCI DSS actually requires
The standard has 12 principal requirements under six headings, as JPMorgan’s PCI guide lays them out:
- Build and maintain a secure network and systems
- Protect account data
- Maintain a vulnerability management program
- Implement strong access control measures
- Regularly monitor and test networks
- Maintain an information security policy
The same guide stresses that these are not a one-time checklist. They work as a cycle: assess where cardholder data exists, remediate weaknesses, then report your compliance. For a gym, the first step does the most work. Once you know exactly where card data lives (the terminal, the website, the member software, a drawer of old forms), you can often remove it from places it never needed to be.
What this looks like on a gym floor
- Network: keep the front-desk payment terminal off the guest Wi-Fi that members use, and change default passwords on routers and terminals.
- Account data: never store full card numbers in notes, emails or spreadsheets. Let your processor hold them as tokens.
- Access: give each staff member their own login, and limit who can issue refunds or see payment records.
- Monitoring: keep software and terminals updated, and review who has access when staff leave.
- Policy: write down a short security policy and train front-desk staff on it.
The official PCI DSS document describes the assessment path: confirm scope, perform the assessment, complete the applicable report, complete the Attestation of Compliance, submit it to whoever requested it, and fix anything that falls short.
Which SAQ does your gym fill out?
Most gyms validate compliance with a Self-Assessment Questionnaire. Which one depends on your payment environment. According to a PCI guide written for fitness businesses, the common matches are:
Your payment setupLikely SAQ
All card handling fully outsourced (for example, a hosted checkout page)
SAQ A
Website that affects the security of the payment transaction
SAQ A-EP
Standalone terminals that qualify (dial-out or IP)
SAQ B or B-IP
Web-based virtual terminal on an isolated computer
SAQ C
Larger chains, or setups that fit nowhere else
SAQ D
Two cautions on reading that table. First, SAQ A is for merchants whose account data functions are completely outsourced to validated third parties, and it does not apply to face-to-face channels. A gym with a card reader at the desk can’t simply use SAQ A for that part of the business. Second, your acquirer ultimately decides which form it wants. Confirm the right one with them.
Your validation level
Visa sorts merchants into four levels by annual transaction volume. Level 1 starts above 6 million Visa transactions and requires a formal report on compliance plus an Attestation of Compliance. Level 4 covers merchants with fewer than 1 million Visa transactions (and fewer than 20,000 Visa eCommerce transactions), and it calls for an SAQ or other validation the acquirer defines.
Here is a simple example. A gym with 800 members billed monthly runs 9,600 recurring charges a year across all card brands, nowhere near a million. Even adding retail and drop-in sales, an independent gym almost always lands in Level 4. Large multi-location operators should ask their acquirer which level applies to them.

If a processor handles your payments, are you off the hook?
No, but you are in a much better position. The PCI Security Standards Council states that PCI DSS applies to any entity handling cardholder data whether it does so directly or through a third-party provider. Merchants who outsource everything still validate compliance, typically through SAQ A, and confirm their obligations with their acquirer or payment brand.
That same page lists what you owe your providers:
- A written agreement with each provider (Requirement 12.8.2)
- Monitoring each provider’s compliance status at least annually (Requirement 12.8.4)
- A clear definition of which security responsibilities are yours and which are theirs
Bank of America’s merchant FAQ puts the practical point well: your business remains responsible through its own practices, and service providers must validate their own compliance each year and provide proof. A compliant terminal in an insecure back office can still lead to a breach.
The upside is real, though. Stripe notes that routing payments through a PCI Level 1 platform removes many of the costly requirements of storing or securing card data, and that tokenized or hosted payment systems can cut audit scope and annual compliance costs considerably. For gyms, this is the main reason to keep card numbers out of your own systems entirely. Our guide to matching Stripe products to dues, sales and setup covers how that choice plays out in practice.
A realistic path to compliance
The PCI guide for fitness businesses suggests an eight-month, four-phase plan. That pace suits a gym that stores or handles card data itself. If you already use hosted, tokenized payments, you can move through it much faster. The sequence is still useful:
- Assess and scope. List every place a card is accepted: desk terminal, website, app, phone, paper. Map where card data flows and decide which SAQ fits.
- Close the big gaps. Segment networks, put firewalls in place, set up strong authentication, and begin staff training.
- Harden and monitor. Apply patches, turn on logging, write an incident response plan, and run vulnerability checks.
- Document and validate. Complete the SAQ and Attestation of Compliance, and submit them to your acquirer.
Bank of America offers merchants a portal that points them to the right SAQ, uses non-technical language and includes vulnerability scanning and security policy templates. Many acquirers run something similar, so look at what yours provides before paying anyone for a separate tool.
A yearly routine
Validation repeats annually. Put a recurring reminder on the calendar and, each year:
- Re-list every place you take card payments, since new tools sneak in (a new class booking page, a new retail kiosk).
- Re-confirm each provider’s compliance status and file the proof.
- Review staff access, and remove anyone who no longer needs it.
- Complete and submit your SAQ and Attestation of Compliance.
- If your setup requires them, schedule vulnerability scans quarterly.
Common gym mistakes that expand your PCI scope
- Paper and spreadsheet card data. Old membership forms with card numbers are the classic problem. Move cardholders onto tokenized storage and shred the rest.
- Payments by text or email. Members sometimes send card details this way. Never accept them, and give staff a script that sends the member to a secure payment link instead.
- Shared logins at the desk. If every front-desk employee uses one account, you can’t show who accessed what.
- Too many payment tools. Separate systems for retail, classes, personal training and dues each add a vendor to vet and a connection to secure.
- Assuming the processor handles everything. Their compliance covers their systems. Your network, devices and people are yours.
Recurring billing carries its own rules beyond PCI, such as disclosure and cancellation practices. Our walkthrough of FTC-compliant recurring gym billing covers that side, and getting recurring payments live in 30 days covers the setup steps. If you collect bank payments, see our notes on ACH payments for gyms.
What does PCI compliance cost a gym?
There’s no single number. Costs depend on your validation level, how many systems touch card data, and what your acquirer charges for compliance programs or non-validation. Gyms that keep card data out of their own environment and use hosted payment pages generally have the lightest workload, because their SAQ is short and their security measures are fewer.

To get a real figure for your gym, look at your merchant statement for monthly PCI or non-compliance fees, and ask your acquirer which SAQ and validation level they expect from you. Those two answers tell you more than any published average.
Our perspective
We hear the same thing from gym owners: payments get bolted on over the years. One tool for dues, another for retail, a spreadsheet for personal training packages, a third system for the website. Every one of those is a vendor you are expected to vet each year and a place card data can end up.
That is why we built Fitness Flow as a single platform. Sales, scheduling, recurring billing and the branded member app live in one place, so there is less to inventory when you scope your PCI work and fewer providers to track under the vendor-management requirements. We also hear that owners lose around 12 hours a week to admin, and compliance paperwork is part of that load.
Our advice: shrink the number of places card data can exist, keep it with a provider that validates compliance every year, and treat PCI as an annual routine instead of a one-off project. Fewer tools makes that routine much easier to keep up.
Louis
Simplify the tools behind your payments
Fitness Flow brings lead tracking, class booking, recurring billing, waivers, the branded member app and reporting into one gym management platform, with integrations to popular payment tools. Plans start at $149 per month for Solo and $349 per month for Studio, and Multi-site is available for groups of locations. Migration support helps you move off a patchwork of separate subscriptions.
See how the plans compare on the Fitness Flow pricing page, or look at what the platform does for gyms.
FAQ
Do small gyms and boutique studios really need PCI compliance?
Yes. Bank of America’s guidance says PCI DSS compliance is required whether you accept five card payments or five million. Smaller gyms usually have simpler requirements, since they fall in the lowest validation level and often complete a short SAQ.
Which SAQ should a gym use?
It depends on how you take payments. Fully outsourced online processing points to SAQ A, qualifying terminals to SAQ B or B-IP, and web-based virtual terminals to SAQ C. Because SAQ A doesn’t cover face-to-face payments, a gym with a front-desk reader should confirm the right form with its acquirer.
If my payment processor is PCI compliant, am I compliant too?
Not automatically. You still validate your own compliance each year, keep written agreements with your providers, and monitor their status at least annually. Their compliance covers their systems, while your network, devices and staff remain your responsibility.
How often do I need to revalidate?
Validation is annual. Some environments also need quarterly vulnerability scans. Use your acquirer’s portal or your processor’s compliance program to track the deadlines.
Is PCI compliance the same as ADA or privacy compliance?
No. PCI covers card data security only. Accessibility and privacy are separate obligations, which we cover in our guides to ADA rules for gyms and data privacy for gyms.
Sources
- PCI Compliance FAQ, Bank of America Merchant Help
- PCI Compliance, Bank of America Merchant Help
- Review PCI Data Security Essentials for Small Merchants, Visa
- PCI DSS SAQ A, PCI Security Standards Council
- Does PCI DSS apply to merchants who outsource all payment processing, PCI Security Standards Council
- Payment Card Industry Data Security Standard v4.0.1
- PCI Compliance Guide, JPMorgan
- How Much Does PCI Compliance Cost for Businesses, Stripe
- PCI Compliance Guide for Gyms and Fitness Centers